
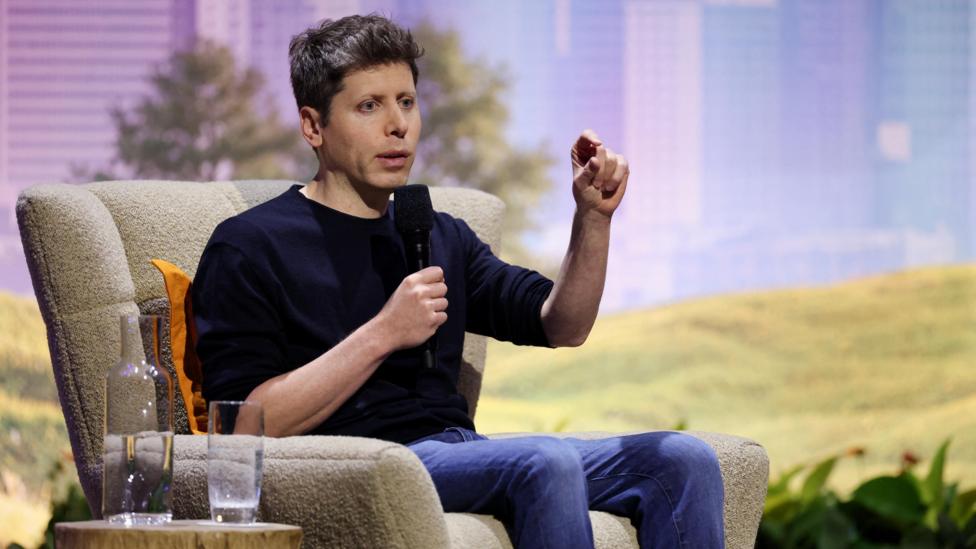
Artificial intelligence executives, led by prominent developers across Silicon Valley, have acknowledged that public anxiety regarding rapid technological advancement is entirely justified while defending industry efforts to build internal safeguards. In recent policy addresses and industry forums, leadership figures emphasized that software developers face substantial commercial and societal incentives to prevent autonomous systems from escaping oversight, despite mounting regulatory pressure from federal watchdogs.
Balancing Public Fear with Industry Self-Regulation
The latest statements reflect a calculated shift in tone among pioneering technology companies attempting to manage growing regulatory scrutiny. Corporate leaders concede that systemic risks spanning economic displacement, algorithmic bias, and autonomous weaponization represent legitimate threats. However, they maintain that market incentives naturally discourage the deployment of hazardous systems, arguing that public confidence remains the primary currency for sustainable commercial growth.
Industry analysts indicate that public trust has deteriorated rapidly following the proliferation of advanced generative models. Consumer advocacy groups continue to demand transparent testing protocols before new models reach enterprise integration. In response, developer coalitions argue that proactive risk mitigation strategies are already embedded within core engineering workflows, serving as a functional counterweight to reckless competitive pressure.
Economic Incentives and Technical Governance
Software developers increasingly argue that building catastrophic systems directly undermines long-term enterprise value. Under this operational model, commercial stability relies on predictable, reliable computation rather than unconstrained model capabilities. Executive teams stress that major software providers cannot sustain enterprise revenue if their foundational models produce widespread legal liabilities, intellectual property violations, or hazardous societal outcomes.
Corporate governance filings reveal that frontier laboratories have expanded internal safety divisions, assigning dedicated teams to red-teaming and adversarial stress testing. These technical protocols aim to identify potential system failures before public release. Yet independent researchers warn that internal oversight structures often yield to competitive pressures when rivals accelerate their public deployment schedules across commercial markets.
Federal Scrutiny and Global Regulatory Frameworks
Legislative bodies and government agencies are moving rapidly to establish enforceable guardrails rather than relying solely on voluntary industry compliance. International policy summits have focused on establishing standardized metrics for evaluating model robustness, computational thresholds, and safety margins. Officials emphasize that self-regulation alone cannot replace statutory oversight, particularly when advanced models interface with critical national infrastructure and financial systems.
State documents highlight ongoing investigations into algorithmic transparency, data privacy compliance, and consumer protection vulnerabilities. Regulatory agencies have warned that existing consumer protection statutes apply directly to automated systems, irrespective of marketing claims regarding emergent capabilities. Compliance specialists note that tech firms must prepare for mandatory external audits, third-party verification, and stringent incident-reporting mandates.
Institutional Responses to Long-Term Systemic Hazards
Academic institutions and independent research foundations continue to publish risk assessments highlighting catastrophic scenarios, ranging from automated disinformation campaigns to uncontrolled biological threat synthesis. These findings have intensified debate regarding open-source release models versus closed commercial APIs. Open-source advocates champion democratization and broad accessibility, whereas enterprise developers argue that strict access controls prevent malicious actors from repurposing powerful algorithms.
Spokespersons from leading artificial intelligence institutions maintain that cross-industry collaboration is essential to establishing baseline technical standards. Collaborative initiatives have begun sharing vulnerability databases, standardizing evaluation benchmarks, and coordinating responses to severe security exploits. These institutional alliances demonstrate a growing consensus that uncoordinated development introduces systemic vulnerabilities that threaten the entire global technology ecosystem.
Future Outlook and Technological Transition
The ongoing tension between rapid commercial deployment and rigorous safety testing will likely define corporate technology roadmaps for the coming decade. As sovereign governments finalize comprehensive legislative frameworks, commercial developers will face increased compliance costs and mandatory reporting burdens. How effectively private industry balances financial incentives with collective safety will ultimately determine whether widespread public skepticism can be transformed into lasting institutional trust.
Moving forward, enterprise deployment strategies will require verifiable proof of safety rather than simple verbal assurances from executive suites. As computational capabilities expand toward more autonomous architectures, independent regulatory oversight and enforceable safety compacts will serve as the definitive measures of accountability for the global technological infrastructure.
