
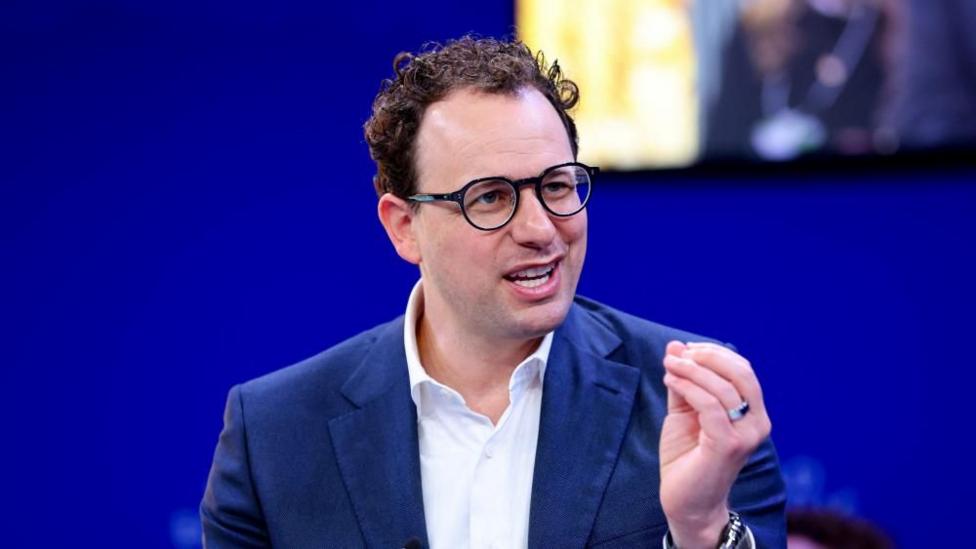
San Francisco tech leader Dario Amodei, chief executive of artificial intelligence firm Anthropic, has formally called on international developers and regulatory bodies to decelerate the deployment of advanced computational models. The appeal highlights growing apprehension among senior scientists that frontier systems could soon unleash severe global security threats if structural safeguards fail to keep pace with rapid technological iteration.
Escalating Catastrophic Risks Prompt Call for Strategic Restraint
Industry executives point to a narrowing window before next-generation neural networks gain autonomous capabilities capable of inflicting widespread societal disruption. Technical dossiers suggest that upcoming releases could potentially aid malicious actors in engineering biological threats, coordinating massive cyberattacks, or destabilizing critical infrastructure networks without requiring advanced specialized human knowledge.
Rather than demanding a permanent moratorium on technical research, the proposal focuses on implementing deliberate pacing mechanisms across commercial laboratories. This measured approach aims to give computer scientists and institutional safety researchers adequate time to develop robust alignment techniques, ensuring complex digital decision-making systems remain strictly within human operational boundaries.
Regulatory Deficits and Institutional Safety Measures
Current legal frameworks across major global economies remain ill-equipped to audit or monitor proprietary software systems operating at unprecedented scales. While several national governments have established specialized evaluation bodies, binding enforcement mechanisms remain largely absent, leaving risk mitigation primarily in the hands of private corporations operating under intense competitive market pressures.
Public policy analysts note that voluntary commitments from corporate technology boards provide insufficient protection against dangerous deployment practices. Without uniform international standards and mandatory red-teaming protocols, competitive economic forces incentivize firms to rush frontier products into commercial distribution before testing teams can exhaustively uncover catastrophic failure modes.
Federal oversight bodies are actively reviewing proposed hardware thresholds, tracking compute clusters, and evaluating supply chain metrics to detect unvetted frontier training runs. State filings suggest legislative committees are drafting statutory frameworks requiring independent safety certification prior to public release, reflecting a dramatic shift from earlier permissive approaches toward tech governance.
Economic Competition Versus Responsible Scaling Policies
Commercial incentives continue to clash directly with calls for developmental caution as billions of dollars flow into private generative computing ventures. Venture capital funds and enterprise clients demand continuous performance enhancements, creating a complex dilemma for safety-focused research entities attempting to balance corporate sustainability with systemic existential risk reduction.
Proponents of deliberate pacing argue that corporate profitability will collapse entirely if an catastrophic systemic failure undermines public trust in automated platforms. Responsible scaling policies establish definitive safety milestones that models must satisfy before acquiring additional computing power, effectively tying capital expenditure to measurable, verifiable alignment metrics.
National Security Implications and International Consensus
Defense planners and intelligence agencies increasingly treat autonomous codebases as strategic assets comparable to defense hardware. National security briefings warn that unilateral deceleration by domestic companies could theoretically grant geopolitical adversaries a temporary development advantage, complicating international efforts to reach enforceable multilateral safety pacts.
Despite these foreign policy hurdles, non-proliferation experts emphasize that catastrophic risks transcend national borders, creating a shared international interest in preventing uncontrolled model deployment. Cross-border scientific working groups have already begun outlining mutual verification protocols modeled after civil aviation safety frameworks and nuclear monitoring agreements.
Diplomatic envoys are currently preparing for upcoming international summits where binding containment strategies and shared compute thresholds will dominate intergovernmental discussions. Officials recognize that uncontrolled computational proliferation poses shared vulnerabilities that require collective diplomatic intervention rather than fragmented, state-level initiatives.
Future Outlook for Global Computing Governance
The coming legislative sessions across North America and Europe will likely determine whether voluntary corporate restraint transitions into comprehensive statutory regulation. Lawmakers face mounting pressure from academic institutions and ethics watchdogs to establish independent auditing boards with authority to pause unverified commercial launches.
Ultimately, the emerging consensus among technical leadership suggests that the trajectory of artificial intelligence cannot rely solely on unchecked corporate competition. As computational architectures grow increasingly sophisticated, the integration of structured delays and safety audits will define whether autonomous technologies safely empower society or destabilize global security.
