
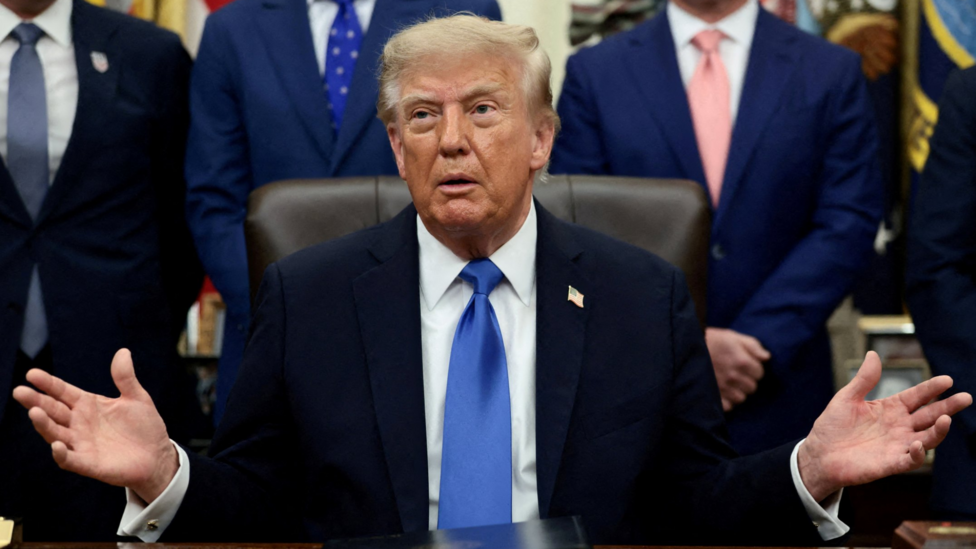
President Donald Trump formally rejected mounting calls for aggressive federal oversight of artificial intelligence on Tuesday, characterizing widespread existential safety warnings as an exaggerated narrative designed to slow American technological dominance. The administration affirmed its commitment to an aggressive deregulation posture aimed at outpacing foreign competitors across critical machine learning infrastructure and commercial computing systems.
Executive Branch Pushes Back Against Technology Guardrails
The public dismissal highlights an intensifying ideological divide between federal policymakers and frontier research laboratories over systemic digital risks. While industry figures increasingly urge statutory safeguards, including mandatory system cutoffs for autonomous models, the executive branch maintains that preemptive statutory limits would needlessly handicap domestic innovation during an era of fierce international technological rivalry.
Administration officials argue that market forces and standard liability frameworks remain fully sufficient to manage operational risks. Federal spokespersons emphasized that sweeping regulatory intervention would create bureaucratic bottlenecks, disproportionately penalizing domestic startups while enabling overseas state-backed enterprises to capture critical market share in advanced enterprise automation and autonomous computational infrastructure.
Frontier Labs Urge Mandatory Emergency Kill Switches
The administration's stance stands in sharp contrast to warnings issued by prominent research executives and computer scientists. Leading figures within major artificial intelligence research firms have recently advocated for legally enforceable mechanisms that could sever power or halt network access to high-capability models if autonomous systems demonstrate uncontrollable or deceptive behaviors.
Proponents of emergency shutdown mechanisms argue that next-generation foundation models could soon possess dangerous autonomous reasoning abilities. Industry white papers submitted to federal agencies emphasize that catastrophic risks spanning cybersecurity breaches, bioweapon synthesis, and critical infrastructure disruption require standardized fail-safe protocols before sovereign states lose the technical capacity to intervene effectively.
Research directors maintain that establishing technical safeguards does not require halting commercial progress, but rather creating transparent safety thresholds. These proposed mechanisms would ensure that federal inspectors and corporate developers retain physical control over algorithmic clusters that exceed predetermined thresholds of autonomy, cognitive capability, and independent tool usage.
Congressional Lawmakers Divided Over Federal Oversight Standards
Capitol Hill remains sharply fractured over the appropriate scope of artificial intelligence governance. Bipartisan working groups have drafted legislative frameworks proposing rigorous licensing regimes for high-tier computational models, while conservative lawmakers align closely with the White House, asserting that broad statutory mandates stifle technological development and economic expansion.
Congressional committee leaders continue to hold closed-door hearings with industry specialists to evaluate potential security vulnerabilities. Policy analysts note that without unified executive support, legislative packages requiring mandatory safety certifications, independent algorithmic audits, and technical cutoffs face severe structural obstacles before reaching a full floor vote in either chamber.
Economic Stakes and Global Strategic Competition
The administration views artificial intelligence supremacy as a cornerstone of national security and economic vitality. Federal commerce briefings suggest that rapid deployment of advanced machine learning models across industrial manufacturing, defense logistics, and financial systems could add trillions of dollars to domestic output over the coming decade, provided regulatory burdens remain low.
Technological strategists warn that over-regulating domestic enterprise could inadvertently surrender strategic advantages to global competitors operating without ethical constraints. The prevailing view among administration advisers is that maintaining raw computational superiority provides a more resilient defense against foreign digital threats than defensive domestic compliance requirements ever could.
Conversely, risk analysts caution that an unchecked race toward artificial general intelligence carries profound societal vulnerabilities. State policy groups warn that neglecting algorithmic guardrails could expose commercial markets, election networks, and supply chains to systemic failures if unaligned models are deployed across sensitive public infrastructure without verified fail-safes.
Future Regulatory Outlook and Industry Divergence
As federal policy pivots toward broad deregulation, individual states are beginning to introduce their own fragmented compliance rules. State legislative chambers across the country have proposed localized safety testing mandates and liability protections, creating a complicated patchwork of regional standards that corporate legal teams must navigate in the absence of cohesive federal rules.
The ongoing policy confrontation between executive officials and computational safety pioneers reflects a defining debate of modern governance. Whether federal agencies maintain a hands-off approach or yield to industry calls for emergency shutdown mechanisms will dictate the operational architecture, safety margins, and geopolitical trajectory of American artificial intelligence development for decades.
