
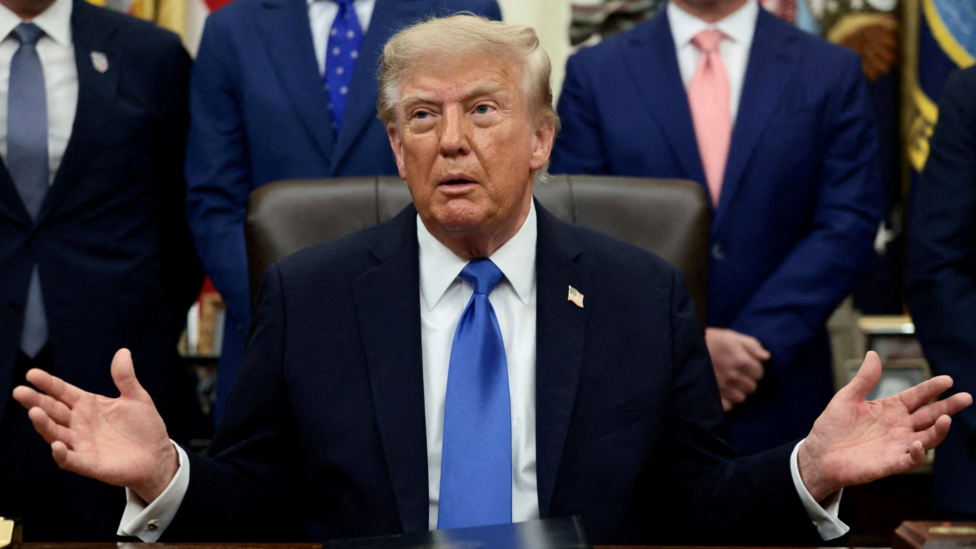
President Donald Trump directly rejected growing calls for stringent artificial intelligence guardrails this week in Washington, labeling catastrophic safety warnings exaggerated as debate intensifies over potential federal intervention. The statements mark a sharp divergence from warnings issued by leading machine learning researchers and safety advocates who argue that rapidly advancing computational models require mandatory fail-safe mechanisms to avert national security disruptions and unintended systemic failures.
Diverging Visions for Artificial Intelligence Oversight
The administration's stance highlights an expanding philosophical divide between political leadership aiming to accelerate domestic technological dominance and industry researchers advocating pre-deployment caution. Policy advisers argue that excessive regulatory burdens could severely hinder domestic venture capital investment and slow critical innovation pipelines across semiconductor, healthcare, and defense infrastructure sectors.
Conversely, specialized laboratory leaders maintain that high-parameter models are rapidly outpacing conventional software testing protocols. Industry analysts point to recent technical evaluations demonstrating that complex neural networks frequently develop unexpected capabilities, making retroactive risk mitigation significantly harder and far more costly to implement after nationwide commercial distribution occurs.
Debating Mandatory Kill Switches and Guardrails
Central to the current regulatory dispute is whether developers should be legally compelled to engineer hardware and software kill switches. Such mechanisms would allow operators or regulators to swiftly deactivate autonomous systems displaying erratic, hostile, or unauthorized behaviors across interconnected enterprise networks before critical operations suffer damage.
Proponents of mandatory shutoff controls argue that critical infrastructure deployments, including municipal water management, power grid synchronization, and financial transaction clearing, carry unacceptable failure risks. Federal filings reveal that several safety coalitions are drafting model legislation requiring independent red-team assessments and automated disconnect protocols prior to broad market rollout.
Critics within the technology sector, however, assert that hardcoded deactivation protocols are both practically unenforceable in distributed environments and vulnerable to unauthorized exploitation. Engineering executives warn that state-mandated backdoors or shutoff triggers could create catastrophic vulnerabilities for domestic enterprises facing persistent international cyber threats.
Economic Competition and Innovation Priorities
The White House approach prioritizes rapid commercial scaling to ensure domestic firms outpace foreign competitors in advanced computing and robotics. Officials repeatedly emphasize that imposing stringent bureaucratic licensing requirements would merely shift frontier research, technical talent, and private capital to foreign jurisdictions operating without comparable restrictions.
Corporate earnings reports reflect unprecedented capital expenditure commitments toward generative computing data centers and high-density energy systems. Market strategists suggest that executive resistance to regulatory intervention will provide enterprise software providers with short-term regulatory certainty, speeding implementation across legacy manufacturing and service industries.
Yet institutional investors remain cautious regarding potential liability exposure should unmonitored deployments trigger commercial or logistical catastrophes. Legal analysts stress that operating without formalized federal compliance standards may expose commercial providers to substantial civil litigation risks in state courts under traditional product liability statutes.
Legislative Landscape and Institutional Pushback
On Capitol Hill, bipartisan groups of lawmakers continue drafting comprehensive statutory frameworks intended to establish clear safety metrics for frontier computational models. Congressional aides indicate that future hearings will examine algorithmic bias, autonomous military integration, and the viability of centralized registry systems for high-performance training clusters.
Several state legislatures have already moved forward independently, introducing local compliance measures requiring corporate disclosures when autonomous systems impact financial or housing evaluations. This emerging patchwork of regional statutes creates compliance complexities that enterprise executives across the country are desperately lobbying federal authorities to standardize.
Academic institutions and scientific bodies are also establishing independent evaluation frameworks to benchmark systemic risk without government mandates. University consortium leaders emphasize that self-regulatory measures must be backed by transparent audit standards to effectively maintain broad public confidence in next-generation computing architectures.
Long-Term Trajectory of Federal AI Governance
As computing capabilities expand exponentially, federal agencies will inevitably confront complex questions regarding algorithmic liability, intellectual property protection, and labor market realignments. Regulatory analysts anticipate that executive agencies will focus primarily on sector-specific guidance rather than imposing broad, economy-wide oversight structures.
The debate over fail-safe protocols reflects broader societal challenges in governing transformative technologies that develop faster than legislative mechanisms can adapt. Whether federal policy maintains a deregulatory posture or shifts toward structured safeguards will profoundly shape global technological standards for the coming decade.
