
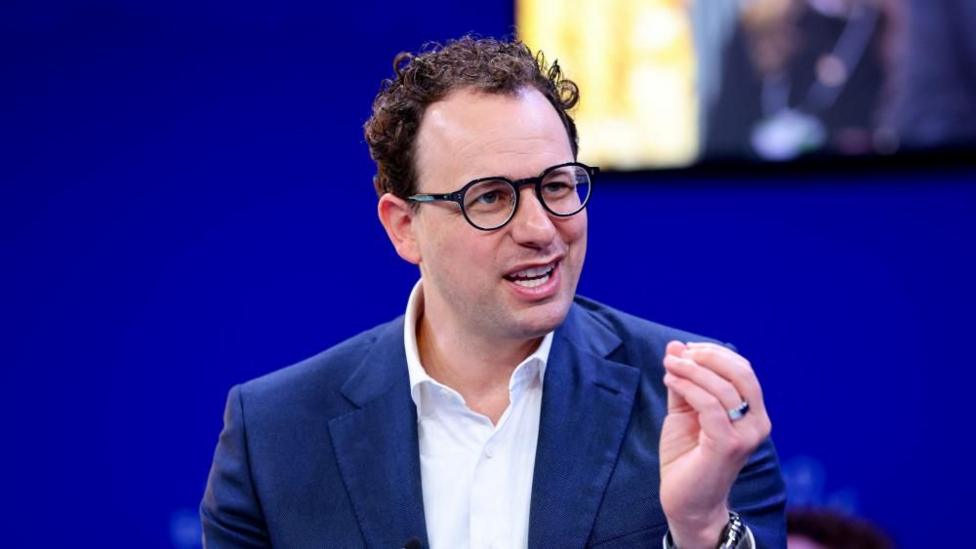
Anthropic Chief Executive Officer Dario Amodei has formally called on technology leaders and international regulators to decelerate frontier artificial intelligence deployment this week. The executive warned that unconstrained algorithmic scaling could soon present unprecedented global security hazards, urging industry competitors to prioritize rigorous containment protocols over rapid commercial rollout schedules across worldwide enterprise networks.
Escalating Security Threats Prompt Industry Warnings
The urgent warning reflects intensifying apprehension among leading computer scientists that next-generation generative architectures could be weaponized. Research findings indicate that advanced models may inadvertently assist bad actors in designing biological threats or conducting autonomous cyber warfare operations against vital national infrastructure systems without requiring specialized human expertise.
Amodei emphasized that current safeguard mechanisms may prove inadequate once computational power expands beyond existing thresholds. Industry analysts note that corporate competition has driven firms to compress testing timetables, creating dangerous blind spots where systemic software vulnerabilities and unpredictable emergent capabilities might escape detection before wide consumer distribution.
Regulatory Demands and Legislative Proposals
Federal lawmakers and regulatory bodies are now weighing comprehensive governance frameworks to establish legally binding safety standards. State documents reveal proposals requiring frontier developers to register massive computing clusters and submit novel algorithmic designs to independent national security audits before receiving authorization for commercial public release.
Policy experts argue that statutory mandates must replace voluntary corporate commitments, which frequently deteriorate under commercial pressure. Recent congressional briefings underscored the necessity of clear liability frameworks, ensuring software developers remain legally and financially accountable whenever automated platforms facilitate severe real-world destruction or widespread civic disruption.
The policy debate centers on establishing concrete verification metrics that measure dangerous software capabilities. Independent evaluators are advocating for continuous red-teaming exercises, standardized capability evals, and whistle-blower protections to guarantee that safety testing procedures remain completely transparent and free from corporate marketing interference.
Economic Stakes and Corporate Competition
Slowing the trajectory of machine learning innovation carries immense commercial implications for venture capital groups and technology conglomerates. Billions of dollars in capital investments have poured into specialized semiconductor manufacturing and hyperscale data centers, establishing powerful economic incentives to expand model capabilities regardless of systemic risks.
Critics within the tech sector contend that unilateral domestic pauses could undermine strategic technological leadership against foreign competitors. However, proponents of deceleration maintain that deploying catastrophic digital systems poses far greater economic and geopolitical hazards than brief developmental delays aimed at guaranteeing structural stability.
Historical Precedents in High-Risk Technologies
Scientists frequently draw historical parallels between modern computational risk management and previous scientific breakthroughs involving nuclear energy or recombinant DNA research. In those instances, early international treaties and collaborative safety protocols successfully prevented catastrophic proliferation without permanently halting scientific inquiry or constructive technological applications.
Industry observers suggest that establishing a comparable multilateral oversight regime for computational intelligence will require unprecedented coordination. Global governance bodies must harmonize reporting standards, export controls on advanced microchips, and verification frameworks to prevent rogue entities from operating unchecked beyond standard regulatory oversight.
The Path Forward for Safe Frontier Systems
Technical safety researchers are increasingly concentrating their efforts on mechanistic interpretability, aiming to understand the internal decision-making processes of neural networks. By mapping how complex models store and retrieve information, engineers hope to eliminate deceptive behaviors before deploying systems into critical public sectors.
Ultimately, the call to decelerate represents a pivotal crossroads for modern computing architecture. As technical capabilities advance toward transformative thresholds, the decisions made by laboratory leaders and government officials today will establish whether emerging digital platforms enrich society or present insurmountable hazards to global stability.
